English
 Arabic
 French
 Spanish
 Portuguese
 Deutsch
 Turkish
 Dutch
 Italiano
 Russian
 Romaian
 Portuguese (Brazil)
 Greek
Intelligent Network Camera Market: Trends, Innovations, and Future Prospects
Other |
2026-08-17 18:37:15
Why Fully Managed SOC Matters for Indian BFSI Security
Banks, financial institutions, and insurance organisations operate technology environments where security visibility and operational continuity are closely connected. Digital banking platforms, internal applications, employee access, connected systems, and customer-facing services can all contribute to a complex security environment.
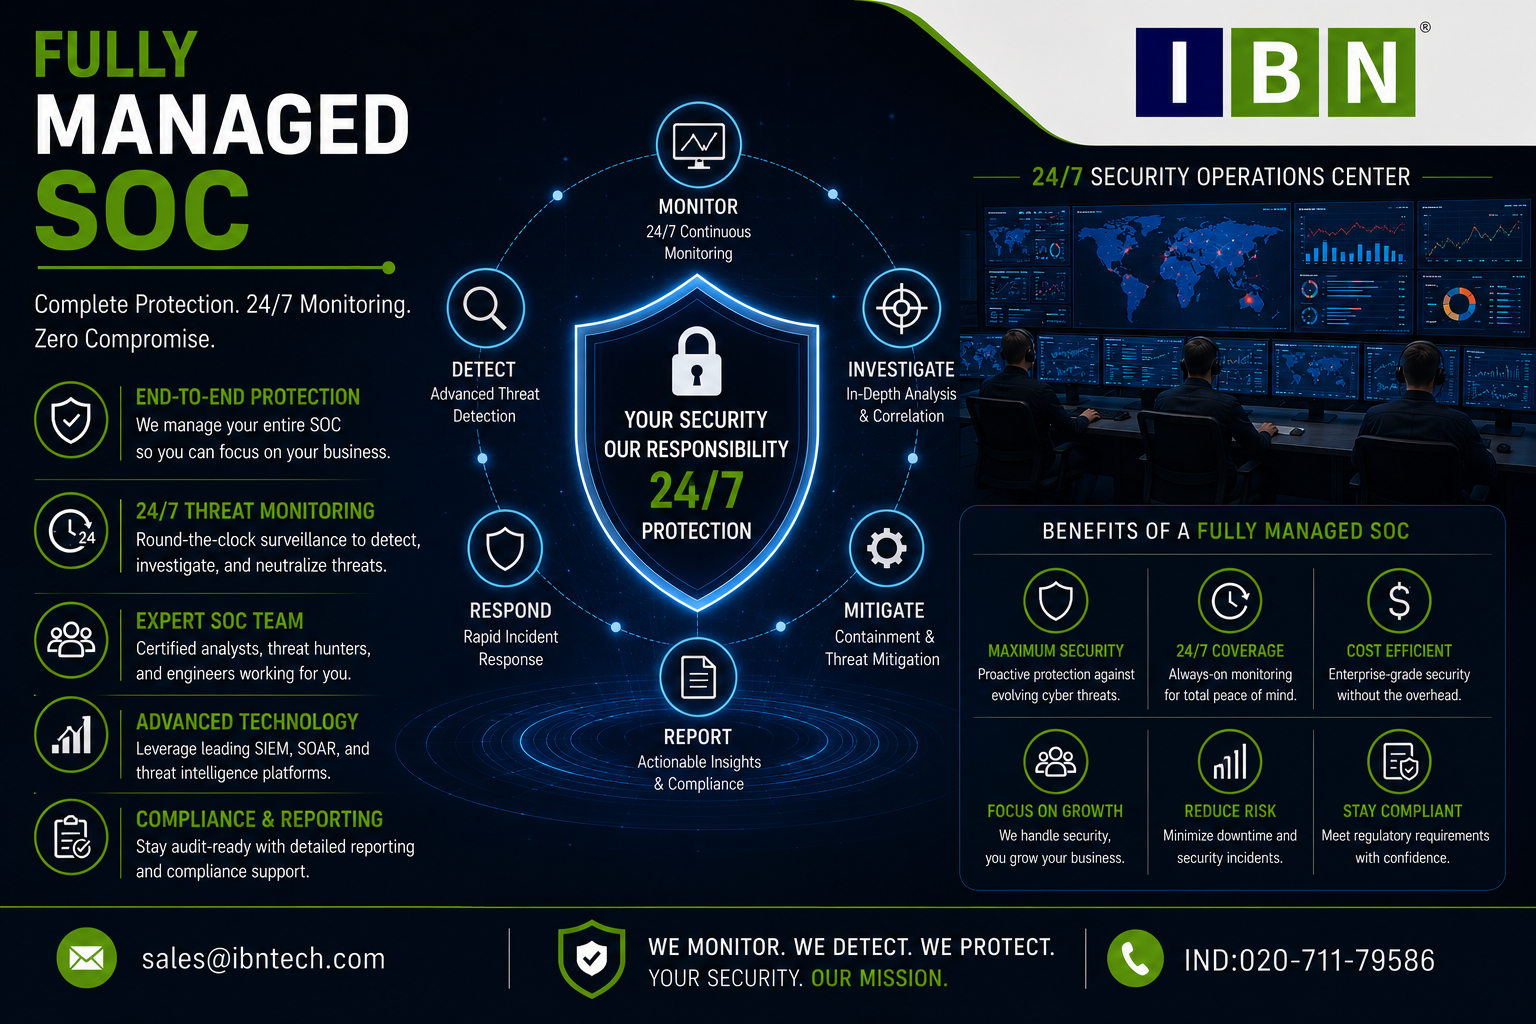
A fully managed soc provides structured security operations support for monitoring, alert analysis, investigation, and escalation. Instead of leaving these activities entirely to internal teams, the organisation can establish an operating model where specialised security operations support works alongside its existing technology and security functions.
For BFSI organisations, this model is relevant not simply because there are more security alerts to review, but because security events need to be assessed within a controlled and clearly defined process.
How Managed SOC Service Providers Support BFSI Security Operations
Managed soc service providers can support BFSI organisations by monitoring security events, analysing alerts, investigating potentially suspicious activity, and escalating relevant findings according to agreed procedures.
The process should connect technical monitoring with organisational responsibilities. An alert that requires further investigation should reach the appropriate security or technology stakeholder, while response decisions remain under the organisation's established governance structure.
This distinction is important for financial organisations. Monitoring and analysis can be supported externally, but accountability for business decisions, risk management, and response remains with the organisation.
The service should therefore be evaluated according to how effectively it fits into existing security operations rather than simply by the number of capabilities listed.
Why BFSI Security Requires More Than Individual Security Tools
Financial organisations commonly use multiple security technologies to protect their environments. Each technology may generate information relevant to security monitoring.
The challenge is creating a coherent process for reviewing that information.
An internal team may need to balance security monitoring with infrastructure operations, application support, access management, compliance activities, and other technology responsibilities. When security events compete for attention, prioritisation becomes an important operational requirement.
A managed SOC model can provide a dedicated process for reviewing security activity and identifying events that warrant investigation.
This does not mean every alert represents a security incident. Effective monitoring involves distinguishing routine activity from events that require additional analysis.
For BFSI organisations, that distinction can help security teams focus attention where investigation is actually required.
What a Fully Managed SOC Adds to BFSI Security Oversight
A fully managed soc can establish a defined operating cycle for security monitoring.
Security events are monitored from relevant environments. Alerts are analysed based on established procedures, and potentially significant activity is investigated. When an event reaches predefined escalation criteria, the appropriate internal stakeholders are notified.
The organisation can then apply its incident management and response procedures.
The model can be represented simply as:
Security activity → Monitoring → Analysis → Investigation → Escalation → Organisational response
This approach creates a connection between security visibility and decision-making.
The precise scope will depend on the organisation's environment and service agreement, but the underlying principle remains the same: monitoring should lead to an actionable process rather than becoming an isolated stream of technical information.
Where Internal-Only Monitoring Can Become Difficult
An internal security team has valuable knowledge of the organisation's systems, applications, users, and business processes. However, maintaining all monitoring activities internally requires appropriate operational capacity and clearly assigned responsibilities.
As environments become more interconnected, security teams may need to review events from multiple technology sources while also managing other security priorities.
Another challenge is maintaining consistency. Monitoring needs to happen continuously according to defined procedures, while investigations need to be documented and escalations handled in a predictable manner.
A managed SOC can supplement this capability by providing dedicated security operations support.
The objective is not to remove the internal team. Instead, the organisation can establish a division of responsibilities between monitoring and analysis activities and the internal decisions required for investigation, remediation, and business response.
What BFSI Organisations Should Evaluate
Selecting a managed security operations model requires attention to both technical and operational factors.
Monitoring scope should be clearly defined. The organisation should understand which systems and security events are included.
Alert analysis should have a documented process. BFSI teams should know how alerts are reviewed and what conditions lead to further investigation.
Escalation procedures should be explicit. Important events need to reach the right internal stakeholders without unnecessary ambiguity.
Reporting should provide useful visibility into security operations. Reports should support the needs of relevant technical and management stakeholders.
Responsibility boundaries should also be established. The organisation and provider should understand who monitors, who investigates, who communicates, and who makes response decisions.
These considerations help turn a managed SOC arrangement into an operational security process rather than simply another outsourced technology service.
A BFSI Scenario: Prioritising an Unusual Access Pattern
Consider a financial organisation where an unusual access pattern generates a security alert.
The alert itself does not establish that a security incident has occurred. It needs to be assessed in context.
A managed security operations team can review the relevant event, investigate according to established procedures, and determine whether the activity warrants escalation.
If escalation criteria are met, the appropriate internal stakeholders can be informed. The BFSI organisation can then assess the event against its own policies, business context, and incident response procedures.
This illustrates why monitoring and investigation need to work together. Detection creates visibility, but structured analysis determines what should happen next.
Governance Should Remain at the Centre
BFSI organisations operate in a highly governed environment, making security oversight an important part of technology management.
A managed SOC should therefore align with the organisation's existing policies and governance processes. Internal stakeholders should understand how security events are documented, escalated, and handled.
Organisations should also establish clear ownership for response decisions. External monitoring support does not remove internal accountability for risk decisions or business impact.
Regular reviews can help determine whether the monitoring scope and escalation model continue to reflect changes in applications, infrastructure, users, and security requirements.
A governance-focused approach also makes it easier for management to understand how security operations support the broader risk-management framework.
Building a Practical Managed SOC Operating Model
Before engaging a provider, BFSI organisations can define the security outcomes they expect from the service.
The organisation should identify critical monitoring requirements, establish escalation thresholds, document internal responsibilities, and determine what reporting stakeholders need.
A practical operating model should address:
These areas create a foundation for evaluating whether the managed service remains aligned with business and security requirements over time.
Compliance Readiness Through Better Security Visibility
Security monitoring can contribute to an organisation's broader compliance and governance activities by providing structured visibility into security events and operational processes.
However, a SOC service should not be treated as a substitute for compliance controls, policies, risk assessments, access governance, or internal oversight.
For Indian BFSI organisations, security operations should work alongside the organisation's wider regulatory and information-security obligations. Monitoring, investigation, escalation, and documentation should therefore be connected to established governance processes.
The exact requirements applicable to an organisation depend on its business model, regulatory position, technology environment, and applicable frameworks.
Turning Security Monitoring Into Operational Awareness
For BFSI organisations, security visibility is most useful when it supports informed operational decisions.
A fully managed soc can provide a structured framework for monitoring security activity, analysing alerts, investigating potentially significant events, and escalating findings to the appropriate internal teams.
The value of the model ultimately depends on how well its processes align with the organisation's technology environment and governance structure.
For Indian financial organisations considering managed security operations, the focus should remain on practical questions: what needs monitoring, how alerts will be assessed, when escalation occurs, who owns response decisions, and how security activity will be reported.
A clearly defined fully managed soc model can help connect continuous security monitoring with the broader security oversight responsibilities of an Indian BFSI organisation.
Contact Us:
IND- 02067680404
IBN Technologies Ltd.
E-mail: - sales@ibntech.com